

Explore how government IT solutions support secure digital services, public sector modernization, system integration, data protection, and resilient public platforms.
A citizen renews a licence at 10:45 p.m. A benefits application moves between departments without paper. None of that feels remarkable anymore, which is exactly why the technology behind it carries more pressure.
Digital government is no longer an optional channel beside the “real” service. For many people, the portal, payment gateway, identity check, and notification system are the service. That changes what agencies need from government IT solutions. Security, integration, recovery, accessibility, and auditability have to work together.
The scale is already visible in India. The Department of Administrative Reforms and Public Grievances reported in its 35th NeSDA Monthly Report, released in April 2026, that States and Union Territories were providing 25,209 e-services. The same report put saturation of 2,124 mandatory e-services at more than 81%.
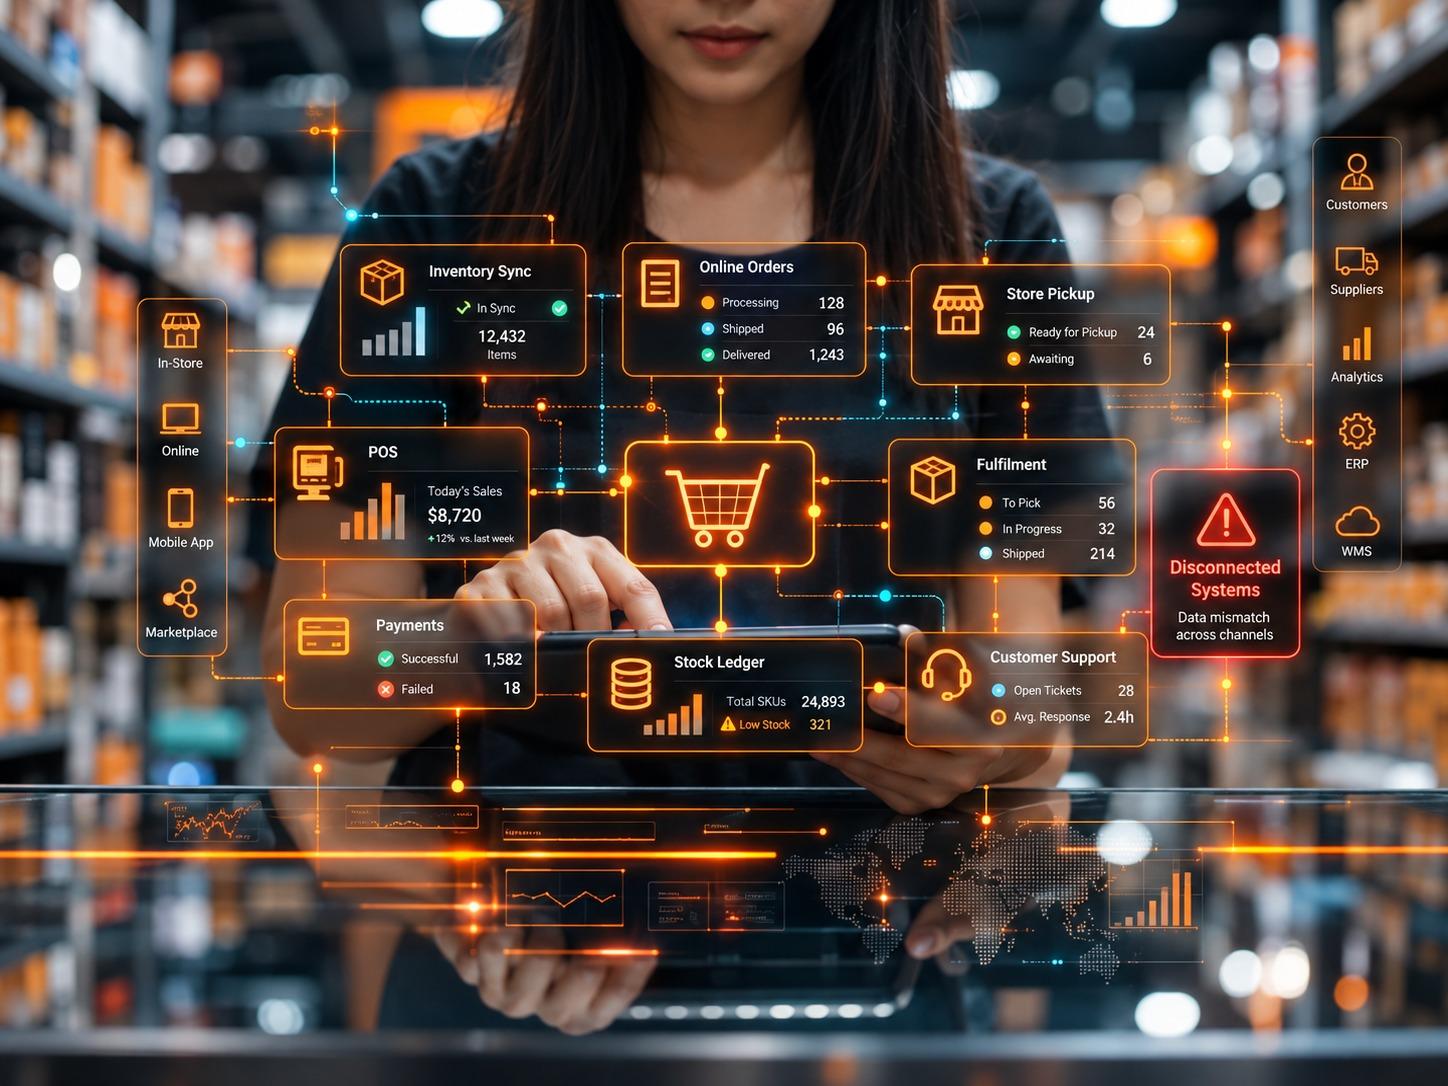
Every new digital service can introduce another identity flow, API, data store, vendor connection, or approval path. We see government IT solutions becoming essential because agencies have to protect a larger environment while keeping services usable.
Why Government IT Solutions Now Start With Service Risk
Infrastructure once felt like a back-office concern. Digital delivery has collapsed that distance.
A failed integration can delay an application. A weak account recovery process can expose personal data. A certificate renewal missed by one team can take a portal offline. A badly designed API can give a partner more access than the job requires. These are technical faults, but the public experiences them as service failures.
Secure digital services need government IT solutions built around the full transaction, not one application at a time. We trace the user task, participating systems, data movement, required proof, and failure path.
Our government work applies that approach for agencies planning safer digital delivery, stronger data controls, and more dependable public platforms.
Secure Digital Services Need More Than A Protected Front End
A modern portal may have multifactor authentication and encrypted traffic, yet still depend on an older case-management system with broad permissions. The visible interface looks current. The deeper transaction may still carry yesterday’s access rules.
That is a common problem in public sector IT modernization. Agencies add digital channels faster than they simplify the systems behind them, leaving duplicate records, manual reconciliation, and fragile point-to-point connections.
Good government IT solutions should reduce those hidden dependencies. The right move may be replacement, safer authentication, a controlled API, better logging, or moving one workflow while leaving the core in place.
Public Sector IT Modernization Has Become A Cybersecurity Job
Cybersecurity teams now protect public-facing applications, identity services, data exchanges, cloud workloads, vendor accounts, and systems built under very different security assumptions.
India’s Ministry of Electronics and Information Technology said in August 2026 that CERT-In tracked 29,44,248 cyber security incidents during 2025, compared with 20,41,360 in 2024. The figure appears in the government release “Government Strengthens Cyber Security Preparedness of Central Government Digital Platforms and Citizen Services.”
Not every incident involved government systems, but the figure shows the environment agencies operate in. Public sector IT modernization has to account for scanning, credential attacks, exposed services, and faster exploitation.
For us, government IT solutions should remain easier to defend after delivery: fewer unmanaged accounts, known owners, documented dependencies, monitored interfaces, tested recovery, and reviewable access.
Identity And Access Need To Follow The Transaction
One of the quickest ways to expose a digital service is to give a user, service account, or partner access that extends beyond the task.
A licensing system may need to verify a person’s identity. It may not need the full record from the identity source. A payment service needs confirmation of a successful transaction, not broad access to the case-management database. A contractor maintaining one application should not inherit permissions across an entire department.
Access works better when it is narrow by design. We map the transaction first, then decide which user or system needs each field, function, or action.
The same thinking applies between applications. Our system integration services focus on controlled data movement, ownership, authentication, and architecture rather than another fragile connection.
CTA: Need Secure Government Systems Without Adding More Complexity?
We can help you connect public services, strengthen access controls, and modernize critical workflows in practical stages without forcing every system into one large replacement programme.
Government IT Solutions Need Connected Data Without Loose Access
Public services often depend on information held by several teams. Copying everything into one place may simplify integration, but it can also expand exposure.
A better design asks what the receiving service actually needs. If one department only needs to confirm eligibility, a verified status may be enough. If a workflow needs an address, there may be no reason to send unrelated financial or identity fields with it.
This is where government IT solutions and data governance meet. Agencies need source owners, defined retention, controlled interfaces, and logs showing when important data moved and why.
Our work on why government digital transformation fails without better system integration looks at these same dependencies from the service-delivery side: disconnected systems, unclear ownership, privacy checks, and continuity all shape whether a digital programme works after launch.
Two Checks Before Connecting Another Public System
- Check the minimum data required. Start with the decision the receiving system must make, then request only the fields or verification needed for that decision.
- Check the failure path. Define what staff and citizens see when an API, identity provider, payment service, or source database becomes unavailable.
Those questions can stop expensive integration problems before development begins.
Public Sector IT Modernization Cannot Ignore Operational Continuity
Government platforms rarely get the luxury of shutting down for a long rebuild. Tax, permits, welfare, licensing, health, transport, records, and internal administrative systems still have users while modernization is underway.
Sequencing is important. Government IT solutions should identify components with the highest service or security exposure, then move work in controlled releases. A programme may begin with identity, integration, a high-risk application, or recovery rather than the oldest platform.
A 2025 audit by the Office of the Auditor General of Canada showed why coordination deserves as much attention as tooling. It found that 119 of 204 federal organisations were not required to use the central cyber security services under review. In one major attack, slow coordination and limited information sharing delayed the government response by 7 days.
The lesson travels: strong products still fail operationally when responsibilities, inventories, escalation routes, or service boundaries are unclear.
Build Modernization Around Dependencies, Not Product Categories
Procurement organises technology into products. Services do not. An online permit might depend on identity, payments, document storage, notification, case management, geospatial data, and an internal approval tool. Replacing the case-management product without tracing the rest can move the bottleneck instead of removing it.
We build government IT solutions around dependencies because outages and security surprises often appear there. Teams should know what calls what, which records are authoritative, where credentials live, and what can fail safely.
A dependency register does not need to become another heavy governance document. We prefer something teams can maintain: service owner, technical owner, upstream systems, downstream systems, data classification, recovery target, vendor dependency, and change window. If nobody can update it after launch, it will quickly become historical.
Government Cybersecurity Solutions Need Visibility Across The Whole Service
Security monitoring gets harder when logs stop at application boundaries. One citizen transaction may pass through six systems while each team sees only its portion.
The ENISA Threat Landscape 2026 found public administration was the most targeted sector in its dataset, representing 32% of targeted organisations. The same 2026 release said more than 48,000 new vulnerabilities received CVE identifiers during 2025, a 22% increase from the previous year.
Agencies cannot patch by headline. A vulnerability in an isolated test tool is not the same operational problem as one in a public-facing identity component used by several services.
Government IT solutions should connect vulnerability information to ownership, exposure, criticality, and compensating controls. Teams can then decide what needs emergency action, a scheduled fix, or retirement.
Our discussion of security, data sovereignty, and AI readiness also applies here. Public systems increasingly use cloud services, analytics, automation, and AI, but those capabilities depend on controlled data locations, strong access paths, and governance that teams can enforce.
Secure Digital Services Also Need Better Architecture For AI
AI is entering public services through search, document processing, fraud review, translation, classification, and internal assistance. Adding a model is often the easy part.
The harder work comes from access. What can the tool retrieve? Can it update a record? Which answer needs human review? What gets logged? Can a team reconstruct which source influenced an output weeks later?
This is another reason government IT solutions cannot be separated from architecture. An AI assistant connected to weak permissions only makes the weakness faster. A model reading duplicated records can return a polished answer built on conflicting information.
We prefer to prepare the service first: identify approved data, define access boundaries, document actions, add review points, and test failures. Public sector IT modernization lets agencies build those controls in before deployment.
CTA: Planning A Safer Digital Government Programme?
We can help your team review system dependencies, secure data flows, integration risks, and modernization priorities before the next public service or AI initiative moves into production.
What Better Government IT Solutions Look Like In Practice
There is no single architecture for every agency. A municipality, regulator, transport authority, and national ministry carry different workloads and risks.
Still, strong government IT solutions tend to show the same practical traits. Teams know who owns critical systems. Access is tied to a task. Integrations are documented. Data has an authoritative source. Monitoring follows transactions across services. Recovery procedures are tested. Modernization has an order, not just a list.
The citizen experience improves too. People submit information once where rules allow, get useful status updates, and see errors that explain what happened.
That is the goal we keep in view at Hubops. Our government IT solutions are not built around replacing technology for its own sake. We use modernization, integration, secure connectivity, cloud architecture, and application work to remove specific weaknesses that affect public delivery.
Final Thoughts
Secure digital government is becoming everyday government. As more services move online, connections between identity, applications, data, payments, vendors, and internal teams become part of public delivery.
Government IT solutions manage that complexity without treating every problem as a new tool purchase. Useful work starts with the service, maps dependencies, narrows access, improves visibility, and protects continuity.
Public sector IT modernization also needs patience in the right places. Some systems can move quickly. Others carry decades of rules and dependencies that deserve staged change. We would rather make those constraints visible early than discover them during cutover.
For Hubops, government IT solutions should leave agencies with fewer hidden dependencies, stronger controls, easier maintenance, and digital services people can use without seeing the work behind them.
Frequently Asked Questions
Why are government IT solutions becoming more important for digital services?
Government IT solutions connect security, applications, data, identity, integration, and infrastructure so agencies can expand online services without creating unmanaged technical or operational exposure internally.
How does public sector IT modernization improve security?
It can remove unsupported components, reduce excessive access, document integrations, strengthen monitoring, and create clearer recovery paths while agencies continue delivering essential public services securely.
What should agencies review before modernizing a government platform?
Teams should review service criticality, system dependencies, data ownership, identity controls, vendor access, recovery requirements, integration paths, accessibility needs, and the operational impact of change
How can system integration improve secure digital government services?
Controlled integration can reduce duplicate data, manual handoffs, and broad system access by defining what information moves, which application owns it, and who can use it.
Where should a government IT modernization programme begin?
Start with services carrying the highest combination of security exposure, operational importance, difficult maintenance, weak recovery, and dependency risk, then sequence changes around continuity carefully.